A popular Android screen recording app that garnered tens of thousands of downloads on Google’s App Store later began spying on its users, including recording microphones and stealing other documents from users’ phones, a cybersecurity firm says. Was.
ESET’s research found that the Android app, “iRecorder – Screen Recorder”, introduced malicious code as an app update nearly a year after it was first listed on Google Play. According to ESET, the code allowed the app to stealthily upload one minute of ambient audio from the device’s microphone every 15 minutes, as well as exfiltrate documents, web pages and media files from the user’s phone.
The app is no longer listed in Google Play. If you have installed the app, you should remove it from your device. By the time the malicious app was pulled from the App Store, it had racked up over 50,000 downloads.
ESET is calling the malicious code AhRat, a customized version of an open source remote access trojan called AhMyth. Remote access trojans (or RATs) take advantage of broad access to a victim’s device and can often include remote control, but can also perform functions similar to spyware and stalkerware.
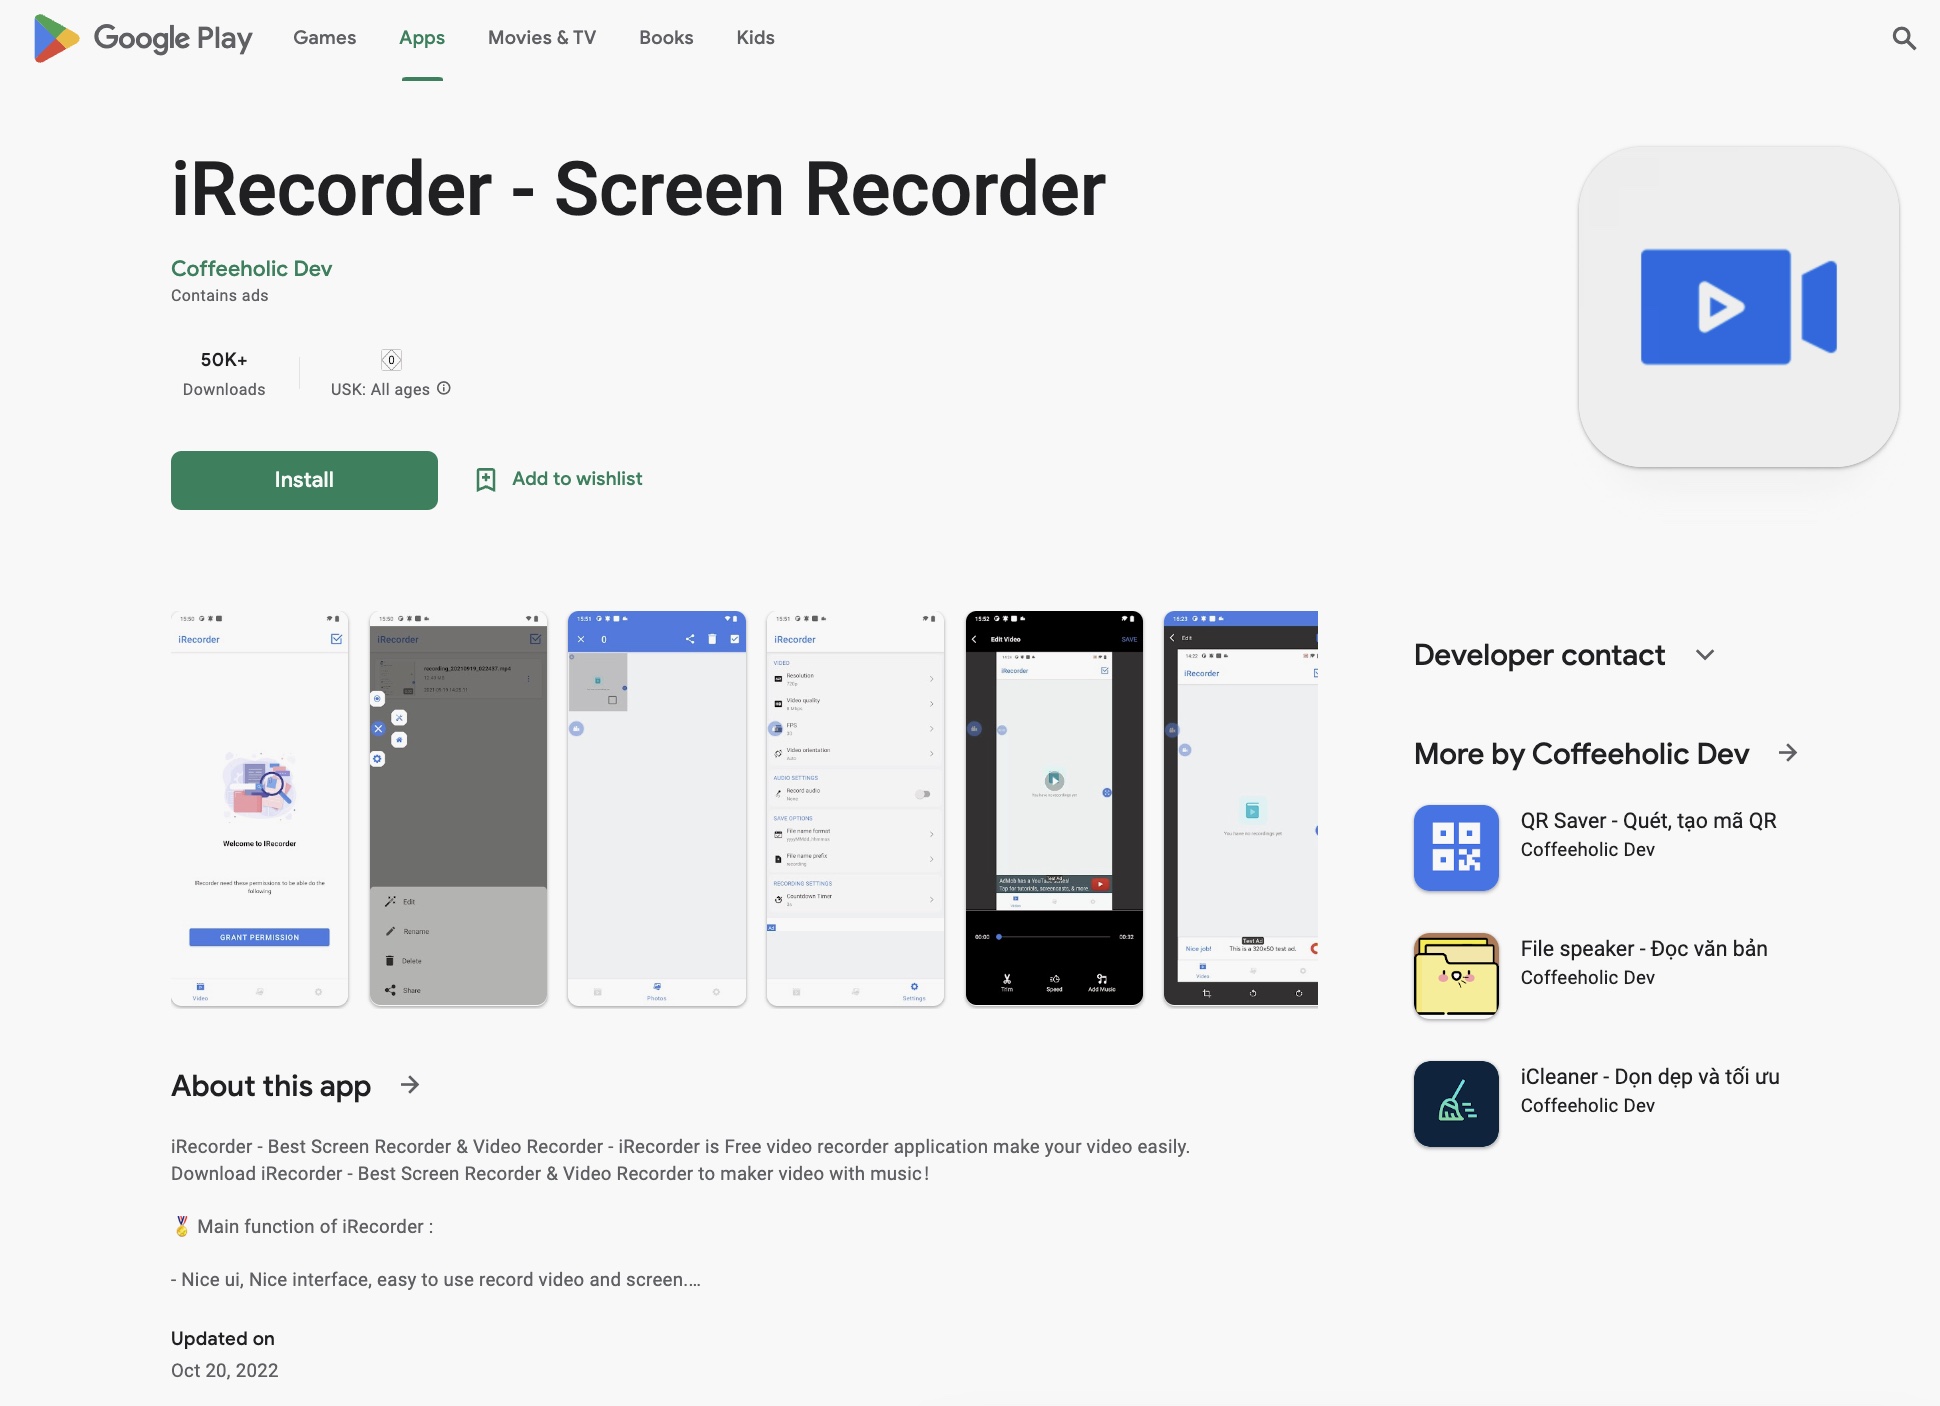
A screenshot of iRecorder listed in Google Play as it was cached at the Internet Archive in 2022. Image Credits: TechCrunch (screenshot)
Lukas Stefanko, a security researcher at ESET who searches for malware, said in a blog post that the iRecorder app did not contain any malicious features when it first launched in September 2021.
Once the malicious AhRat code was pushed as an app update to existing users (and new users who would download the app directly from Google Play), the app began surreptitiously accessing the user’s microphone and collecting the user’s phone data. Started uploading to a server controlled by malware. operator. Stefanko said that the audio recording “fit within a previously defined app permissions model”, noting that the app was by nature designed to capture screen recordings of the device and to provide access to the device’s microphone. Will say
It’s not clear who planted the malicious code – whether a developer or someone else – or for what reason. TechCrunch emailed the developer’s email address before the app was pulled from the list, but has yet to hear back.
Stefanko said the malicious code could be part of a wider espionage campaign — where hackers sometimes work on behalf of governments or for financially motivated reasons to collect information on their chosen targets. He added that “it was rare for a developer to upload a legitimate app, wait nearly a year, and then update it with malicious code.”
It’s not unusual for bad apps to hit the App Store, nor is this the first time AhMyth has made its way into Google Play. Both Google and Apple screen apps for malware before listing them for download, and sometimes actively act to pull apps when they could put users at risk. Last year, Google said it blocked more than 1.4 million privacy-violating apps from accessing Google Play.


