Last week, the US Federal Trade Commission (FTC) published a report according to which cryptocurrency scammers have duped Americans of over $1 billion since 2021. Cryptocurrency scams are rampant on social media sites, as well as on messaging apps like Telegram. Scams often trade in the names of cryptocurrency-related celebrities, such as Jack Dorsey and Elon Musk. However, scams are just one way for bad actors to steal cryptocurrencies. Rather than trick unsuspecting victims into handing over their crypto, some cybercriminals turn to malware to hunt down the crypto themselves.
Researchers at Confident have published their findings detailing a widespread malware campaign the researchers are calling Seaflower. The campaign is targeted at users of four different cryptocurrency wallets on iOS and Android: MetaMask, Coinbase Wallet, ImToken Wallet and TokenPocket Wallet. Threat actors for seaflowers spoke Chinese, looking at code comments written in Chinese, along with several other indicators noted by the researchers. The threatening actor appears to be most likely targeting other Chinese speakers, who have run an SEO poisoning campaign that has hit most search results from the Chinese-based Baidu search engine. SEO poisoning campaigns take advantage of search engine optimization (SEO) techniques to promote malicious websites to top search results for legitimate websites or services.
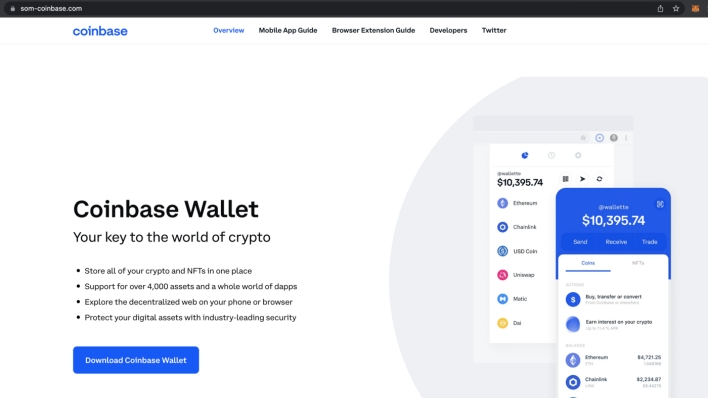
 Malicious clone of the Coinbase Wallet website (source: conf)
In this case, the threat actors have successfully promoted malicious clones of websites for legitimate cryptocurrency wallets. Malicious websites appear similar to their legitimate counterparts, but they are hosted on domains that are controlled by dangerous elements. Malicious websites include download buttons for Android and iOS apps, but instead of redirecting users to the Google Play Store or Apple App Store, the buttons attempt to side-load apps to users’ devices.
 Installation process for malicious iOS profile (source: confidant,
In the case of Android, websites only offer an APK file, which users can download and install on their own. However, Apple doesn’t allow easy app side-loading like Android, so instead of serving up installation packages, websites try to set up provisioning profiles on iOS devices. These profiles come with developer keys that allow side-loading of malicious apps.
Once installed, malicious apps are visible and act similarly to the legitimate cryptocurrency wallet apps they imitate. However, malicious apps come with backdoors that log wallet seed phrases, addresses and balances and send that information to the threat actors behind the campaign. Threatened actors can then use seed phrases to complete the account recovery process and gain access to funds in the victims’ wallets. In some cases, backdoor code is encrypted, which means that anyone who inspects the code for malicious behavior uses cryptographic tools involved to decrypt the malicious code before finding out what the code does. keys must be used.
To avoid falling victim to such a malicious app campaign, iOS users should not allow external provisioning profiles to be installed on their devices, and Android users should only install apps from trusted sources. All Wallet apps targeted by this particular attack can be found in the Google Play Store and Apple App Store, so users should download and install them there.
Researchers have provided hashes for one malicious Android app and distributed it to all four malicious iOS apps as part of a Seaflower campaign, to identify other malicious apps.
coinbase wallet android app
APK of SHA-256:
83dec763560049965b524932dabc6bd6
252c7ca2ce9016f47c397293c6cd17a5
Coinbase Wallet iOS App
The SHA-256 of the .ipa was analyzed:
2334e9fc13b6fe12a6dd92f8bd65467cf
700f43fdb713a209a74174fdaabd2e2
metamask ios app
The SHA-256 .ipa file analyzed:
9003d11f9ccfe17527ed6b35f5fe33d28
e76d97e2906c2dbef11d368de2a75f8
imToken Wallet iOS App
The SHA-256 of the .ipa was analyzed:
1e232c74082e4d72c86e44f1399643ff
b6f7836805c9ba4b4235fedbib8bdca
TokenPocket iOS Wallet
The SHA-256 of the .ipa file was analyzed:
46002ac5a0caaa2617371bdddbdbc7eca
74cd9cb48878da0d3218a78d5be7a53a


